Cybersecurity Blog

Cybersecurity Research from the Front Lines

Threat research, infrastructure analysis, and operational guidance from the Team Cymru intelligence team, drawn from the global network visibility we maintain across the internet.

Who
Team Cymru's own threat analysts and researchers, writing from the investigations they run.
What
Named threat actors, mapped command-and-control infrastructure, ransomware toolkit teardowns, and the pivot methodology behind them. 150+ posts and counting.
How
Sourced from Team Cymru's own internet-scale network telemetry. We analyze what we see directly, not third-party feeds or aggregated reporting.
When
New analysis every week, plus rapid posts when a campaign breaks.
Why
So defenders get operational detail they can act on inside a SOC or intel workflow. Published in full, with no gate and no registration wall.
Filter
Sorted Newest first
Annika Martins

From Serengeti to Serengeti III: What Three INTERPOL Operations Reveal

Incident Response & Preemptive Defense
October 22, 2026
INTERPOL’s Operation Serengeti has led to 3,677 arrests across three operations since 2024. What changed from Serengeti to III, and what it means for defenders.
Will Thomas

LegionRelay: Ukraine Targeted by Five Previously Unidentified C2 Servers

Threat Actor, Campaign & Infrastructure Intelligence
October 14, 2026
See how threat hunting in Team Cymru Scout surfaced five previously unreported LegionRelay C2 servers tied to a Russia-aligned campaign targeting Ukraine.
Scott Fisher

Relaying to the Frontier

Threat Actor, Campaign & Infrastructure Intelligence
September 22, 2026
Team Cymru uncovered self-hosted LLM gateways relaying pooled credentials to frontier models like Claude, enabling model distillation and abuse.
From the disk to the flows: ransomware infrastructure analysis of Akira, DragonForce, Clop, and other ransomware gangs
Will Thomas

From the Disk to the Flows: Ransomware Infrastructure Analysis

Malware & Ransomware Analysis
September 15, 2026
A year of incident response data reveals how Akira, DragonForce & Clop build ransomware infrastructure — and how defenders can hunt it.
The transaction is the last step, not the first: spotting fraud attack patterns earlier with threat intelligence

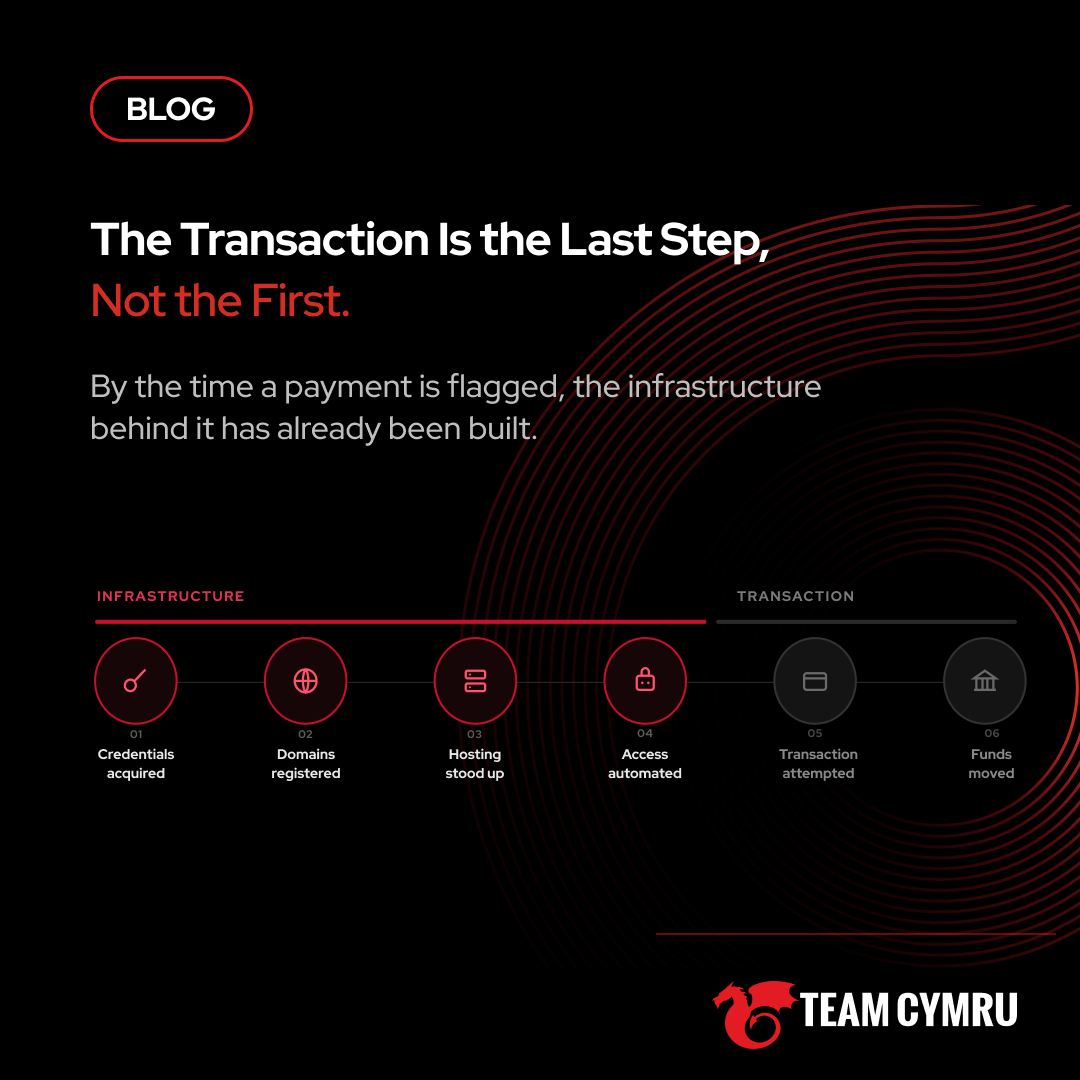
The Transaction Is the Last Step, Not the First

Fraud, Phishing & Supply Chain Risk
September 2, 2026
Waiting for the transaction to catch fraud? You're already too late. Learn how tracking attack patterns in threat intelligence stops actors early.
Cl0p Til You Drop: Cl0p ransomware threat intelligence research on managed file transfer attack campaigns
Eli Woodward

Cl0p Til you Drop - 6 Years, 10 Campaigns, 8 Zero-Days

Malware & Ransomware Analysis
August 12, 2026
Analyze Cl0p ransomware's history of targeting MFT systems. Discover their attack pattern in threat intelligence to improve cyber attack surface reduction.
Behind the Panels: validating ShinyHunters phishing panel infrastructure through network telemetry
Stephen Campbell

Behind the Panels: Validating ShinyHunters Cluster A Infrastructure Through Network Telemetry

Threat Actor, Campaign & Infrastructure Intelligence
August 5, 2026
Use network telemetry to validate cyber threat actors' phishing infrastructure. Track ShinyHunters clusters and defend against SaaS data exfiltration.
Josh Picolet

From C2 Detection to Possible Victim Identification

Malware & Ransomware Analysis
July 27, 2026
Discover how to transition from C2 detection to possible victim identification. Improve your cyber incident response by tracking attacker infrastructure to compromised systems.
Abigail Lorion

Modernizing Incident Response: 4 Steps to Bulletproof Your Windows Logging

Threat Reports & Intelligence Briefings
July 14, 2026
Improve your cyber incident response steps with our guide to bulletproof Windows logging. Discover incident response tools and how AI streamlines DFIR.
Abigail Lorion

Cybercrime Doesn't Reinvent Itself. It Optimizes.

Malware & Ransomware Analysis
June 29, 2026
Discover how AI threat intelligence reveals cybercriminals' true tactics. Learn why agentic AI and automated threat detection are reshaping cybersecurity.
Abigail Lorion

The Unclosed Gap: Why the 2026 DBIR Proves the Decisive Battle Happens Before the First Internal Alert

Attack Surface & Exposure Visibility
May 27, 2026
The 2026 DBIR reveals 88% of threats are external. Learn how Team Cymru's Pure Signal closes the visibility gap before internal alerts trigger.
Stephen Campbell

Targeting the Defense Industrial Base: What Network Telemetry Reveals About Nation-State Pre-Positioning

Attack Surface & Exposure Visibility
April 29, 2026
Discover how nation-states target the Defense Industrial Base via pre-positioning. Learn why network telemetry is crucial to detect these hidden cyber threats.

Stay in the loop

Stay current with Team Cymru insights

Get the latest research, articles, and threat intelligence resources, delivered straight to your inbox.