Team Cymru Blog

Cybersecurity Research from the Front Lines

Threat research, infrastructure analysis, and operational guidance from the Team Cymru intelligence team, drawn from the global network visibility we maintain across the internet.

Who
Team Cymru threat analysts and researchers, with a named byline on technical posts.
What
Named threat actors, mapped command-and-control infrastructure, ransomware toolkit teardowns, and the pivots behind them.
How
Sourced from Team Cymru’s own internet-scale network telemetry, not third-party feeds or aggregated reporting.

Research Library

Find research by threat, problem, or role

Every article carries the same Team Cymru tags as the rest of the site. Stack filters to narrow fast, or tap a category on any card.

Annika Martins

From Serengeti to Serengeti III: What Three INTERPOL Operations Reveal

Incident Response & Preemptive Defense
October 22, 2026
INTERPOL’s Operation Serengeti has led to 3,677 arrests across three operations since 2024. What changed from Serengeti to III, and what it means for defenders.
Takedown
Malicious Infrastructure
Threat Actor Infrastructure
Ransomware
Phishing
Broader Security Audience
Director of Threat Intelligence
Government
Will Thomas

LegionRelay: Ukraine Targeted by Five Previously Unidentified C2 Servers

Threat Actor, Campaign & Infrastructure Intelligence
October 14, 2026
See how threat hunting in Team Cymru Scout surfaced five previously unreported LegionRelay C2 servers tied to a Russia-aligned campaign targeting Ukraine.
C2 Infrastructure
Nation-State
Threat Actor Infrastructure
Phishing
Malware
Threat Intelligence Analyst
Threat Hunter
Government
Healthcare
Scott Fisher

Relaying to the Frontier

Threat Actor, Campaign & Infrastructure Intelligence
September 22, 2026
Team Cymru uncovered self-hosted LLM gateways relaying pooled credentials to frontier models like Claude, enabling model distillation and abuse.
Malicious Infrastructure
Threat Actor Infrastructure
Nation-State
Data Exfiltration
CISO
Threat Intelligence Analyst
Technology
From the disk to the flows: ransomware infrastructure analysis of Akira, DragonForce, Clop, and other ransomware gangs
Will Thomas

From the Disk to the Flows: Ransomware Infrastructure Analysis

Malware & Ransomware Analysis
September 15, 2026
A year of incident response data reveals how Akira, DragonForce & Clop build ransomware infrastructure — and how defenders can hunt it.
Ransomware
C2 Infrastructure
Data Exfiltration
Malicious Infrastructure
SOC Analyst
Threat Hunter
All Verticals
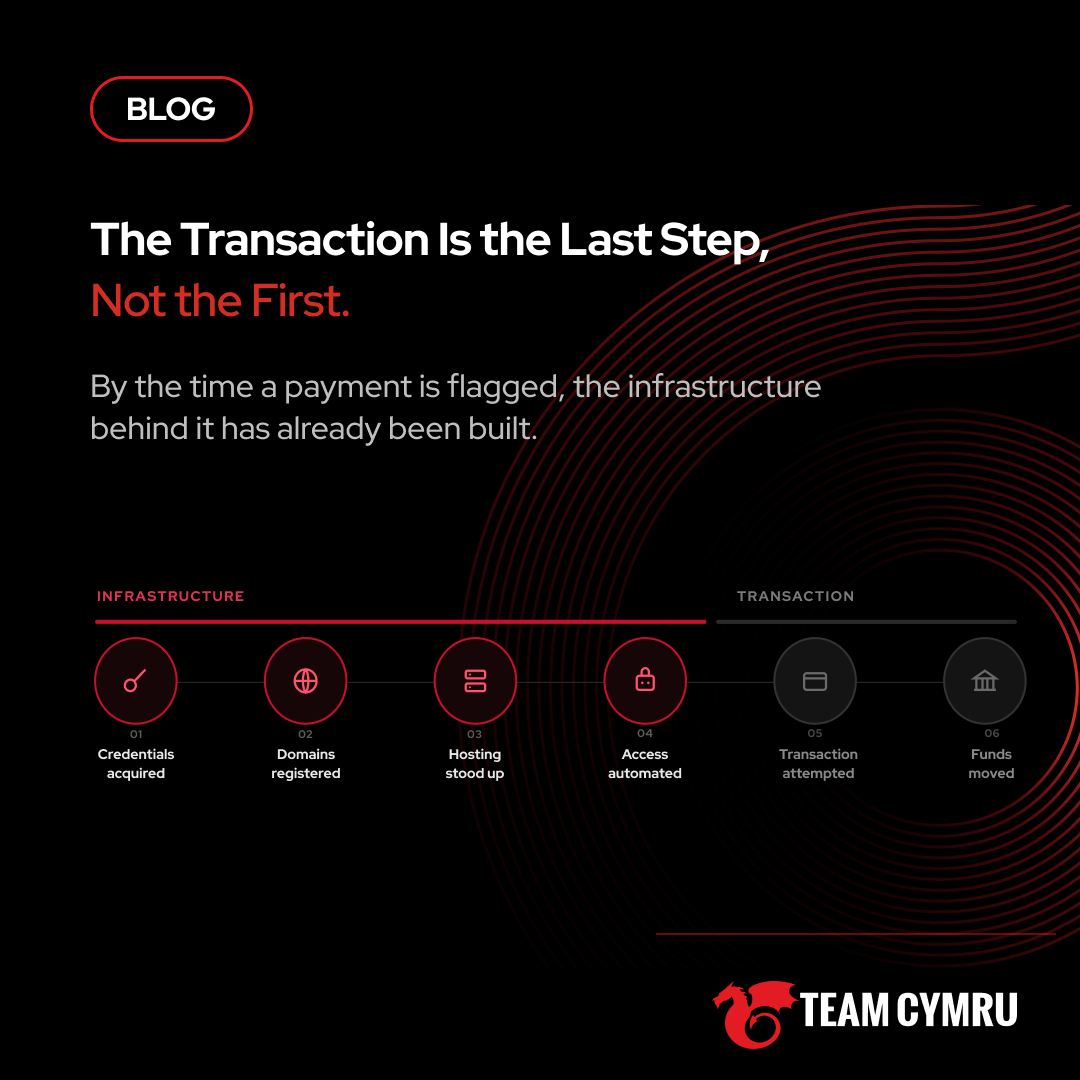
The transaction is the last step, not the first: spotting fraud attack patterns earlier with threat intelligence

The Transaction Is the Last Step, Not the First

Fraud, Phishing & Supply Chain Risk
September 2, 2026
Waiting for the transaction to catch fraud? You're already too late. Learn how tracking attack patterns in threat intelligence stops actors early.
Threat Actor Infrastructure
Malicious Infrastructure
Proactive Threat Intelligence
Preemptive Defense
Visibility Gaps
Chief Fraud Officer
Threat Intelligence Analyst
Financial Services
Payment systems
Cl0p Til You Drop: Cl0p ransomware threat intelligence research on managed file transfer attack campaigns
Eli Woodward

Cl0p Til you Drop - 6 Years, 10 Campaigns, 8 Zero-Days

Malware & Ransomware Analysis
August 12, 2026
Analyze Cl0p ransomware's history of targeting MFT systems. Discover their attack pattern in threat intelligence to improve cyber attack surface reduction.
Ransomware
Zero-Day
Exploitation
Preemptive Defense
Threat Intelligence Analyst
Incident Responder
All Verticals
Behind the Panels: validating ShinyHunters phishing panel infrastructure through network telemetry
Stephen Campbell

Behind the Panels: Validating ShinyHunters Cluster A Infrastructure Through Network Telemetry

Threat Actor, Campaign & Infrastructure Intelligence
August 5, 2026
Use network telemetry to validate cyber threat actors' phishing infrastructure. Track ShinyHunters clusters and defend against SaaS data exfiltration.
Phishing
Threat Actor Infrastructure
Malicious Infrastructure
Data Exfiltration
Proactive Threat Intelligence
Threat Intelligence Analyst
Threat Hunter
All Verticals
Josh Picolet

From C2 Detection to Possible Victim Identification

Malware & Ransomware Analysis
July 27, 2026
Discover how to transition from C2 detection to possible victim identification. Improve your cyber incident response by tracking attacker infrastructure to compromised systems.
Malware
Malicious Infrastructure
Ransomware
Botnets
C2 Infrastructure
Malware Researcher
Incident Responder
All Verticals
Abigail Lorion

Modernizing Incident Response: 4 Steps to Bulletproof Your Windows Logging

Threat Reports & Intelligence Briefings
July 14, 2026
Improve your cyber incident response steps with our guide to bulletproof Windows logging. Discover incident response tools and how AI streamlines DFIR.
Real-Time Intelligence
Proactive Threat Intelligence
Visibility Gaps
Finished Intelligence Limitations
Preemptive Defense
CISO
Broader Security Audience
All Verticals
Abigail Lorion

Cybercrime Doesn't Reinvent Itself. It Optimizes.

Malware & Ransomware Analysis
June 29, 2026
Discover how AI threat intelligence reveals cybercriminals' true tactics. Learn why agentic AI and automated threat detection are reshaping cybersecurity.
Malware
Malicious Infrastructure
Ransomware
Botnets
C2 Infrastructure
Malware Researcher
Incident Responder
Technology
Abigail Lorion

The Unclosed Gap: Why the 2026 DBIR Proves the Decisive Battle Happens Before the First Internal Alert

Attack Surface & Exposure Visibility
May 27, 2026
The 2026 DBIR reveals 88% of threats are external. Learn how Team Cymru's Pure Signal closes the visibility gap before internal alerts trigger.
Malicious Infrastructure
Visibility Gaps
Third-Party Risk
Proactive Threat Intelligence
Real-Time Intelligence
Security Architect
CISO
All Verticals
Stephen Campbell

Targeting the Defense Industrial Base: What Network Telemetry Reveals About Nation-State Pre-Positioning

Attack Surface & Exposure Visibility
April 29, 2026
Discover how nation-states target the Defense Industrial Base via pre-positioning. Learn why network telemetry is crucial to detect these hidden cyber threats.
Exploitation
Visibility Gaps
Malicious Infrastructure
Third-Party Risk
Proactive Threat Intelligence
Security Architect
CISO
All Verticals
Eli Woodward

Unmasking DPRK Cyber Threat Actors: Fake IT Worker Infrastructure & Post-Exposure Analysis

Threat Actor, Campaign & Infrastructure Intelligence
April 22, 2026
Uncover how DPRK cyber threat actors use fake IT schemes, Astrill VPN, and freelance platforms to infiltrate networks. Learn to spot these advanced persistent threats.
Real-Time Intelligence
Visibility Gaps
Finished Intelligence Limitations
Preemptive Defense
Proactive Threat Intelligence
CISO
Threat Intelligence Analyst
Technology
Cyber security intelligence analysis of attacks on edge devices amid growing vulnerabilities
Eli Woodward

Cyber Security Intelligence: Analysis of Edge Devices Amid Growing Vulnerabilities

Threat Reports & Intelligence Briefings
April 2, 2026
Cisco, Ivanti & Fortinet edge device attacks are rising. Read our cybersecurity intelligence on cybersecurity trends and attack patterns.
Real-Time Intelligence
Proactive Threat Intelligence
Visibility Gaps
Finished Intelligence Limitations
Preemptive Defense
CISO
Broader Security Audience
Technology
Will Thomas

Stranger Strings: Yurei Ransomware Operator Toolkit Exposed

Malware & Ransomware Analysis
April 1, 2026
Analyze the Yurei double extortion ransomware campaign, including its toolkit, attack lifecycle, and key tactics used by operators.
APT
Orb Networks
Malicious Infrastructure
Threat Actor Infrastructure
Proactive Threat Intelligence
Threat Intelligence Analyst
Threat Hunter
Telecommunications
Will Thomas

Industrial Cybersecurity Risks from Internet-Exposed ICS Devices

SOC Enablement & Intelligence Enrichment
March 25, 2026
Industrial cybersecurity analysis of exposed ICS and OT devices. Discover how attackers target critical infrastructure and how defenders can detect exposed systems.
Phishing
Malicious Infrastructure
Real-Time Intelligence
Compromised Hosts
C2 Infrastructure
SOC Manager
Security Architect
All Verticals
Jeremy Bender

From Developer to Product Owner: The Fundamental Shifts from Generative AI

Securing AI & Limits of Machine Learning
March 23, 2026
Generative AI handles the plumbing. Learn how AI threat intelligence tools empower analysts to outpace threat actors and become true product owners.
Zero-Day
Exploitation
Supply Chain Attacks
Visibility Gaps
Malicious Infrastructure
Security Architect
Threat Intelligence Analyst
Technology

Team Cymru Partners with DOJ to Disrupt World’s Largest IoT DDoS Botnets

Incident Response & Preemptive Defense
March 20, 2026
Team Cymru partners with the DOJ to dismantle Aisuru, KimWolf, JackSkid & Mossad botnets. See how global network visibility and community-driven intel stopped 30 Tbps attacks.
Takedown
Dark Web Monitoring
Preemptive Defense
Proactive Threat Intelligence
Malicious Infrastructure
Incident Responder
CISO
All Verticals
Will Thomas

The Beast Returns: Analysis of a Beast Ransomware Server

Real-Time Threat Detection & Signals
March 18, 2026
Explore our latest threat intelligence report on Beast Ransomware. See the exact incident response tools and TTPs used by operators to bypass EDR and delete backups.
Real-Time Intelligence
Proactive Threat Intelligence
Preemptive Defense
Malicious Infrastructure
Compromised Hosts
SOC Manager
All Verticals
Jeremy Bender

Duaine Labno on Digital Investigations and Corporate Threat Intelligence

Threat Reports & Intelligence Briefings
March 16, 2026
Explore how digital investigations support corporate threat intelligence, fraud response, and cyber threat investigation with Duaine Labno of TIG Risk Services.
Proactive Threat Intelligence
Real-Time Intelligence
Visibility Gaps
Finished Intelligence Limitations
Preemptive Defense
Threat Intelligence Analyst
CISO
Government
Jeremy Bender

Cybersecurity Incident Response at Thermo Fisher: How the Ransomware Landscape Has Evolved

Incident Response & Preemptive Defense
March 9, 2026
Explore how ransomware and incident response have evolved with Matt McKnew of Thermo Fisher. Learn about the shift to RaaS and the rise of DPRK fake IT worker scams.
C2 Infrastructure
Malicious Infrastructure
Threat Actor Infrastructure
APT
Proactive Threat Intelligence
Threat Intelligence Analyst
Threat Hunter
All Verticals
Will Thomas

GRIMBOLT C2 Infrastructure Recon: Pivoting From One IP to a Mapped Cluster

Threat Actor, Campaign & Infrastructure Intelligence
March 5, 2026
Explore how to Map GRIMBOLT C2 infrastructure linked to UNC6201 by pivoting from one IP using WHOIS, PDNS, ports, and X509 certificate fingerprints.
C2 Infrastructure
Malicious Infrastructure
Threat Actor Infrastructure
APT
Proactive Threat Intelligence
Threat Intelligence Analyst
Threat Hunter
All Verticals
Jeremy Bender

What Helping Secure SMBs Shows About Attack Trends

Threat Reports & Intelligence Briefings
March 3, 2026
Explore SMB ransomware and the latest cybersecurity trends with Alex Bovicelli of Tokio Marine HCC. Learn why securing initial access vectors is the key to proactive defense
Real-Time Intelligence
Proactive Threat Intelligence
Visibility Gaps
Finished Intelligence Limitations
Preemptive Defense
CISO
Broader Security Audience
Technology
Will Thomas

Tracking CyberStrikeAI Usage

Threat Actor, Campaign & Infrastructure Intelligence
March 2, 2026
Discover how CyberStrikeAI is revolutionizing AI-augmented offensive security. Explore its ties to Chinese state-sponsored actors and learn to detect it with NetFlow.
Supply Chain Attacks
Third-Party Risk
Visibility Gaps
Finished Intelligence Limitations
Preemptive Defense
CISO
Threat Intelligence Analyst
All Verticals
Jeremy Bender

What Cyber Insurance Claims Reveal About Real Cyber Risk

Malware & Ransomware Analysis
February 26, 2026
Learn how to reduce cybersecurity risks by analyzing ransomware attack trends and attacker behavior, featuring insights from Daniel Woods of Coalition.
Malware
Ransomware
Botnets
C2 Infrastructure
Compromised Hosts
Malware Researcher
Incident Responder
All Verticals

Team Cymru Partners with INTERPOL in Coordinated Operation Red Card 2.0

Malware & Ransomware Analysis
February 24, 2026
Team Cymru's NetFlow-powered intelligence supports INTERPOL’s Operation Red Card 2.0, disrupting international cyber fraud and malicious infrastructure.
Botnets
Malware
Ransomware
C2 Infrastructure
Compromised Hosts
Threat Intelligence Analyst
Malware Researcher
All Verticals
Jeremy Bender

Fraud Intelligence at Stripe: Inside the Financial Fraud Kill Chain

Fraud, Phishing & Supply Chain Risk
February 23, 2026
Learn how Stripe’s Vincent Passaro applies fraud intelligence to the financial fraud kill chain, breaking down account takeover and how to proactively defend.
Visibility Gaps
Finished Intelligence Limitations
Preemptive Defense
Proactive Threat Intelligence
Real-Time Intelligence
CISO
Threat Intelligence Analyst
Technology

Protecting Critical National Infrastructure (CNI) through extended global visibility

Incident Response & Preemptive Defense
February 17, 2026
Adversaries are pre-positioning for destructive attacks on CNI. Learn how to track nation-state threat actors and ORB networks to harden the OT boundary "left of boom."
Takedown
Malicious Infrastructure
Preemptive Defense
Proactive Threat Intelligence
Threat Actor Infrastructure
Incident Responder
CISO
All Verticals
Will Thomas

Tracking ORBs on Singapore's Telecommunications Networks

Threat Reports & Intelligence Briefings
February 11, 2026
APT attacks by UNC3886 target Singapore telecom using ORB networks. Learn practical ORB tracking techniques to uncover hidden infrastructure with Scout.
Real-Time Intelligence
Proactive Threat Intelligence
Visibility Gaps
Finished Intelligence Limitations
Preemptive Defense
Threat Intelligence Analyst
CISO
All Verticals
Jeremy Bender

How AI-driven Threat Detection is Reshaping Threat Intelligence

AI-Driven Threats & Autonomous Security
February 10, 2026
Hear Fortinet’s Aamir Lakhani explain the role of AI in cybersecurity and how AI-driven threat detection is reshaping modern threat intelligence.
Visibility Gaps
Finished Intelligence Limitations
Preemptive Defense
Proactive Threat Intelligence
Real-Time Intelligence
CISO
Threat Intelligence Analyst
Government
Eli Woodward

MediaLand Isn't Dormant: The Reality of Active OFAC-Sanctioned Infrastructure

Malware & Ransomware Analysis
February 4, 2026
OFAC sanctions compliance goes beyond policy—sanctioned bulletproof hosting like MediaLand AS206728 remains an active risk for financial services.
Malware
Ransomware
Botnets
C2 Infrastructure
Compromised Hosts
Malware Researcher
Incident Responder
All Verticals
Jeremy Bender

Payment Fraud Detection: How ATO and Phishing Kits Drive Modern Abuse

Fraud, Phishing & Supply Chain Risk
February 3, 2026
Blake Butler of PayPal explains modern payment fraud detection, key payment fraud trends, and how ATO account takeover impacts platforms at scale.
Phishing
Supply Chain Attacks
Third-Party Risk
Malicious Infrastructure
Botnets
Chief Fraud Officer
Chief Risk Officer
Payment systems
Kyle Contorno

Operationalize Pure Signal™ in OpenCTI

Threat Reports & Intelligence Briefings
January 30, 2026
Enhance your threat hunting in OpenCTI with Team Cymru’s Pure Signal™ data. Learn how to use dedicated Scout connectors for deep enrichment, infrastructure mapping, and automated STIX relationship graphing.
Real-Time Intelligence
Proactive Threat Intelligence
Visibility Gaps
Finished Intelligence Limitations
Preemptive Defense
CISO
Broader Security Audience
Technology
Jeremy Bender

From Raw Intelligence to Validation: Thoughts on Operationalizing MITRE from a Cyber Threat Intelligence Director

SOC Enablement & Intelligence Enrichment
January 28, 2026
Stop siloing roles. Learn how to operationalize MITRE ATT&CK at a granular level to deprioritize vulnerabilities and build smarter, AI-assisted CTI workflows.
Proactive Threat Intelligence
Visibility Gaps
Finished Intelligence Limitations
Preemptive Defense
Real-Time Intelligence
Threat Intelligence Analyst
CISO
All Verticals
Will Thomas

Scattered Spider Attacks | Infrastructure and TTP Analysis

NetFlow & Traffic Intelligence
January 21, 2026
An in-depth analysis of Scattered Spider attacks, detailing the group’s infrastructure usage and TTPs to help defenders detect and disrupt activity earlier.
DDoS
Real-Time Intelligence
C2 Infrastructure
Threat Actor Infrastructure
Malicious Infrastructure
Threat Hunter
Threat Intelligence Analyst
All Verticals
Jeremy Bender

Reducing Friction in Cyber Threat Intelligence: Views from a Director of Advanced Cyber Practices

Incident Response & Preemptive Defense
January 20, 2026
Learn how Casey Beaumont (Marsh McLennan) reduces incident response friction through unified leadership and discover the 4 critical questions for vendor breach assessments.
Phishing
Malicious Infrastructure
Supply Chain Attacks
Third-Party Risk
Botnets
Chief Fraud Officer
Chief Risk Officer
Technology
Jeremy Bender

Cybersecurity in the Public Sector: Two CISOs’ Views on the Future of Threat Intelligence

Incident Response & Preemptive Defense
January 16, 2026
Hear how public sector CISOs think about cybersecurity. Michael Moore, CISO of Arizona’s Secretary of State, joins the Future of Threat Intelligence podcast.
Preemptive Defense
Proactive Threat Intelligence
Malicious Infrastructure
Threat Actor Infrastructure
Real-Time Intelligence
Incident Responder
CISO
All Verticals
Jeremy Bender

Team Cymru and OpenCTI: Better Together for Threat Intelligence

SOC Enablement & Intelligence Enrichment
January 14, 2026
Accelerate triage and automate threat hunting with the Team Cymru and OpenCTI integration. Combine global visibility with open-source orchestration for faster defense.
Nation-State
Orb Networks
Malicious Infrastructure
Threat Actor Infrastructure
APT
Threat Intelligence Analyst
Threat Hunter
All Verticals
Will Thomas

Analysing Carding Infrastructure

SOC Enablement & Intelligence Enrichment
January 9, 2026
A cybercrime intelligence analysis of carding operations, detailing the infrastructure, hosting providers, and network patterns used to support carding activity.
Proactive Threat Intelligence
Real-Time Intelligence
Compromised Hosts
C2 Infrastructure
Visibility Gaps
Threat Hunter
Threat Intelligence Analyst
Technology
Jeremy Bender

RADAR Offers Full External Asset Discovery at the Click of a Button

Attack Surface & Exposure Visibility
January 5, 2026
Stop chasing unknown assets. Learn how RADAR provides a full footprint of internet-exposed assets and CVE context in minutes using a single search.
Third-Party Risk
Real-Time Intelligence
Exploitation
Malicious Infrastructure
Phishing
Chief Fraud Officer
Chief Risk Officer
All Verticals
Jeremy Bender

Team Cymru Supports INTERPOL in Coordinated Operation Across Africa as Part of Operation Sentinel

Incident Response & Preemptive Defense
December 22, 2025
Team Cymru partners with INTERPOL in Operation Sentinel to dismantle BEC and ransomware networks across Africa. See how 573 arrests and $3M in recoveries were made.
Takedown
Botnets
DDoS
Preemptive Defense
Proactive Threat Intelligence
Incident Responder
CISO
All Verticals
Eli Woodward

The Indictment Is the IOC: Using Legal Records to Hunt DPRK Remote Workers

Threat Actor, Campaign & Infrastructure Intelligence
December 18, 2025
Stop hunting for North Korean malware and start hunting for North Korean behavior. See how Eli Woodward uses criminal indictments and Team Cymru’s global telemetry to surface DPRK remote worker infrastructure by identifying subtle TTP patterns.
Third-Party Risk
Phishing
Supply Chain Attacks
Malicious Infrastructure
Botnets
Chief Fraud Officer
Chief Risk Officer
All Verticals
Jeremy Bender

Query Scout in Synapse Enterprise With New Power-Up for Team Cymru

SOC Enablement & Intelligence Enrichment
December 17, 2025
Instantly run Team Cymru Scout queries on the Pure Signal™ data ocean directly within Synapse Enterprise. See how to hunt for phishing infrastructure, analyze communication patterns, and unpack malicious IPs for frictionless, confident analysis.
Malicious Infrastructure
Threat Actor Infrastructure
APT
Proactive Threat Intelligence
Real-Time Intelligence
Threat Intelligence Analyst
Threat Hunter
All Verticals

From Discovery to Attribution, RADAR Makes Threat Hunting Seamless

Threat Hunting & Detection Engineering
December 11, 2025
Learn how RADAR’s pivot feature automatically generates queries in Scout, allowing analysts to move from infrastructure discovery to threat attribution seamlessly.
Phishing
Supply Chain Attacks
Third-Party Risk
Malicious Infrastructure
Botnets
Chief Fraud Officer
Chief Risk Officer
Financial Services
Jeremy Bender

RADAR Takes the Guess Work Out of Vulnerability Exposure Management

Attack Surface & Exposure Visibility
December 4, 2025
Stop manual asset inventory. RADAR automatically discovers all internet-facing infrastructure and filters for CISA KEVs within seconds. Get a prioritized, actionable list of risks. Learn how.
Exploitation
Malicious Infrastructure
Visibility Gaps
Third-Party Risk
Proactive Threat Intelligence
Security Architect
CISO
All Verticals
Jacomo Piccolini

Team Cymru and Abusix Partner to Eradicate Botnets

Real-Time Threat Detection & Signals
December 3, 2025
Team Cymru's threat intelligence and Abusix's reporting join forces to close the loop on botnet infections. Learn how the partnership systematically eradicates Mirai.
Visibility Gaps
Real-Time Intelligence
Proactive Threat Intelligence
Preemptive Defense
Malicious Infrastructure
SOC Manager
All Verticals
Jeremy Bender

Minimize Partner Risk with RADAR's Third-Party Infrastructure Mapping

Fraud, Phishing & Supply Chain Risk
December 2, 2025
Stop guessing about partner security. RADAR, powered by PureSignal, maps all third-party infrastructure for 100% visibility. Get real-time vulnerability insights without noisy active scans. Learn more
Malware
Malicious Infrastructure
Threat Actor Infrastructure
APT
Proactive Threat Intelligence
Threat Intelligence Analyst
Threat Hunter
All Verticals
Jeremy Bender

With RADAR, Never Worry About Losing Sight of Exposed Assets

SOC Enablement & Intelligence Enrichment
November 19, 2025
Stop losing sight of exposed assets and shadow IT. RADAR provides instant, complete visibility into your entire digital footprint and third-party suppliers, without noisy scanning. Learn how to get started today.
Real-Time Intelligence
Compromised Hosts
C2 Infrastructure
Visibility Gaps
Proactive Threat Intelligence
Threat Intelligence Analyst
SOC Manager
All Verticals
Jeremy Bender

Team Cymru Supports Europol to Takedown of Three Key Cybercriminal Tools as Part of Operation Endgame

Incident Response & Preemptive Defense
November 14, 2025
Team Cymru provided critical data to Europol, leading to the massive disruption of over 1,000 malicious servers and the arrest of a major cybercriminal. See the full Operation Endgame report.
Malicious Infrastructure
Compromised Hosts
Threat Actor Infrastructure
Real-Time Intelligence
Visibility Gaps
Security Architect
Threat Intelligence Analyst
All Verticals
Kyle Contorno

No Scans. No Noise. Just Complete Exposure Visibility

Incident Response & Preemptive Defense
November 12, 2025
The infrastructure you don't know about will hurt you. RADAR delivers complete, passive asset discovery using real network traffic. Stop active scanning risks.
Takedown
Malware
Malicious Infrastructure
Preemptive Defense
Proactive Threat Intelligence
Incident Responder
CISO
All Verticals

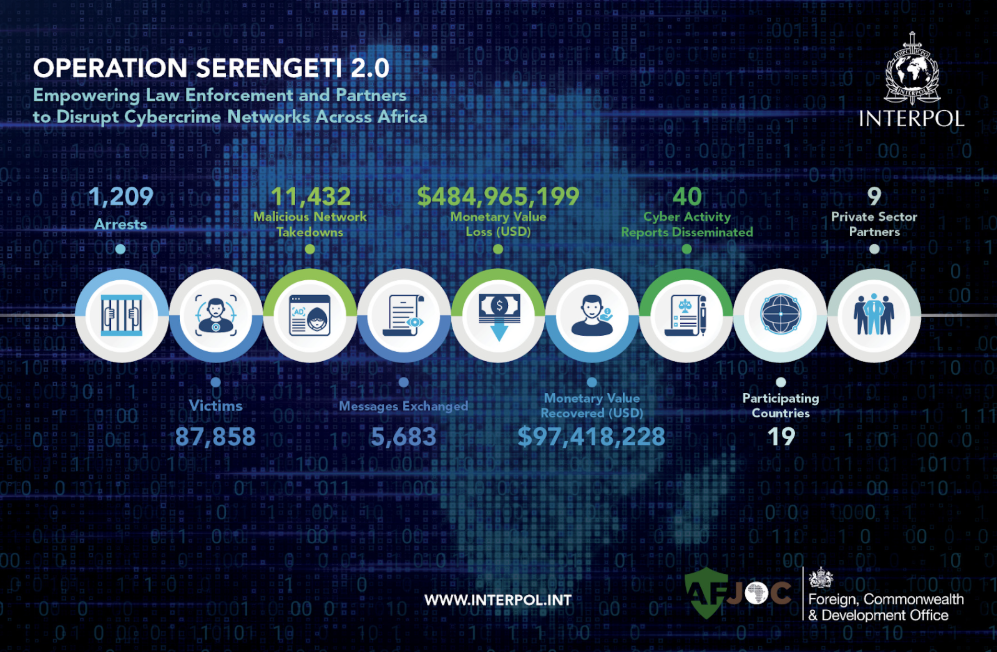
Team Cymru Supports INTERPOL’s Operation Serengeti 2.0 to Dismantle Cybercrime Networks Across Africa

Incident Response & Preemptive Defense
August 26, 2025
Team Cymru supported INTERPOL's Operation Serengeti 2.0, which led to 1,209 arrests and dismantled 11,432 malicious infrastructures across Africa.
Takedown
Dark Web Monitoring
Preemptive Defense
Proactive Threat Intelligence
Malicious Infrastructure
Incident Responder
CISO
Government
Lewis Henderson

Supercharge Threat Hunting: Team Cymru Pure Signal™ Scout Now Integrated with Google SecOps

SOC Enablement & Intelligence Enrichment
August 11, 2025
Team Cymru's Pure Signal Scout now integrates with Google SecOps, adding internet-scale NetFlow context to investigations, threat hunting, and response.
C2 Infrastructure
Data Exfiltration
Compromised Hosts
Ransomware
Visibility Gaps
SOC Manager
Threat Hunter
All Verticals
Will Thomas

Fingerprinting Malware C2s with Tags

Malware & Ransomware Analysis
August 4, 2025
This blog is written for threat analysts, defenders, and CTI teams who use our Scout platform—but even if you’re not a user today, it offers practical insight into how advanced research teams fingerprint C2 infrastructure, and how you might apply similar methods using your tools.
APT
Malicious Infrastructure
Threat Actor Infrastructure
Proactive Threat Intelligence
Real-Time Intelligence
Threat Intelligence Analyst
Threat Hunter
All Verticals
tcblogposts

Team Cymru Tags Explained: Powering Faster, Smarter Threat Intelligence

Cloud & Application Security
August 1, 2025
Discover how Team Cymru Tags deliver real-time context to analysts, enabling faster triage, better threat detection, and automation-ready intelligence. Learn more.
DDoS
Zero-Day
Exploitation
Supply Chain Attacks
Compromised Hosts
Security Architect
All Verticals
Eli Woodward

ToolShell, SharePoint, and the Death of the Patch Window

Cloud & Application Security
July 8, 2025
This blog explores this week's zero-day exploit targeting Microsoft SharePoint, now referred to as ToolShell, caught organizations off guard.
Threat Actor Infrastructure
Malicious Infrastructure
APT
Proactive Threat Intelligence
Real-Time Intelligence
Threat Intelligence Analyst
Threat Hunter
All Verticals
Will Thomas

Supply Chain & CTI

Cloud & Application Security
July 8, 2025
This blog explores how cyber threat intelligence (CTI) must change and support a new approach to supply chain risk.
Zero-Day
Exploitation
Supply Chain Attacks
Compromised Hosts
Visibility Gaps
Security Architect
Technology
Will Thomas

Uncovering DPRK Remote Workers: Detecting Hidden Threats Through Internet Telemetry

Malware & Ransomware Analysis
June 30, 2025
This blog explores unpacks key insights and explains how internet telemetry can be used to detect these threats in the real world.
Malware
C2 Infrastructure
Malicious Infrastructure
Ransomware
Botnets
Malware Researcher
Incident Responder
All Verticals
S2 Research Team

Inside DanaBot’s Infrastructure: In Support of Operation Endgame II

Incident Response & Preemptive Defense
May 22, 2025
This blog explores DanaBot a "malware-as-a-service" and how collaboration across the security community can lead to real progress against threat actors
Supply Chain Attacks
Third-Party Risk
Phishing
Malicious Infrastructure
Botnets
Threat Intelligence Analyst
Chief Fraud Officer
All Verticals
tcblogposts

Understanding the Federal Compliance Landscape

Malware & Ransomware Analysis
March 12, 2025
Explore how federal agencies can align compliance mandates like NIST SP 800-171, CMMC, and FISMA with proactive threat intelligence for stronger security.
Ransomware
Malware
Botnets
C2 Infrastructure
Compromised Hosts
Incident Responder
Malware Researcher
Healthcare
Andrew Korty

Team Cymru Achieves ISO 27001 Re-Certification for Third Consecutive Year

Incident Response & Preemptive Defense
March 11, 2025
Team Cymru earns ISO 27001 re-certification for the third year, reinforcing its commitment to security, compliance, and protecting customer data. Learn more.
Takedown
Ransomware
Malware
Phishing
Dark Web Monitoring
Incident Responder
CISO
Government
Wassim Tawbi

New innovation helps Security Teams gain faster threat insights

API, Platform & Hybrid Visibility Risk
March 5, 2025
Team Cymru's Insights Feed helps security teams cut through noise, reduce false positives, and gain real-time, actionable threat intelligence for faster response.
Real-Time Intelligence
Visibility Gaps
Proactive Threat Intelligence
Malicious Infrastructure
Preemptive Defense
Threat Intelligence Analyst
Security Architect
All Verticals
David Monnier

Top 10 Predictions Shaping the Future of Cybersecurity in 2025 According to 35+ Experts

Attack Surface & Exposure Visibility
February 22, 2025
Explore the top 10 cybersecurity predictions for 2025, based on insights from industry leaders shaping the future of threat intelligence and security strategy.
Compromised Hosts
Visibility Gaps
Malicious Infrastructure
Third-Party Risk
Proactive Threat Intelligence
Security Architect
CISO
All Verticals
David Monnier

Splunk's Security Strategist on Building Effective Threat Hunting Programs

Threat Hunting & Detection Engineering
February 15, 2025
Splunk’s David Bianco shares threat hunting tips, team-building strategies, and how to use red teaming to improve detection capabilities and security operations.
Proactive Threat Intelligence
Threat Actor Infrastructure
Malicious Infrastructure
C2 Infrastructure
Real-Time Intelligence
Threat Hunter
Threat Intelligence Analyst
All Verticals
David Monnier

Google's Head of Security Architecture Shares Framework for Protecting AI Systems

Real-Time Threat Detection & Signals
February 11, 2025
Google’s Head of Security Architecture shares a real-world framework for protecting AI systems from evolving threats like model poisoning and prompt injection.
Real-Time Intelligence
Proactive Threat Intelligence
Preemptive Defense
Malicious Infrastructure
Compromised Hosts
Threat Intelligence Analyst
All Verticals
S2 Research Team

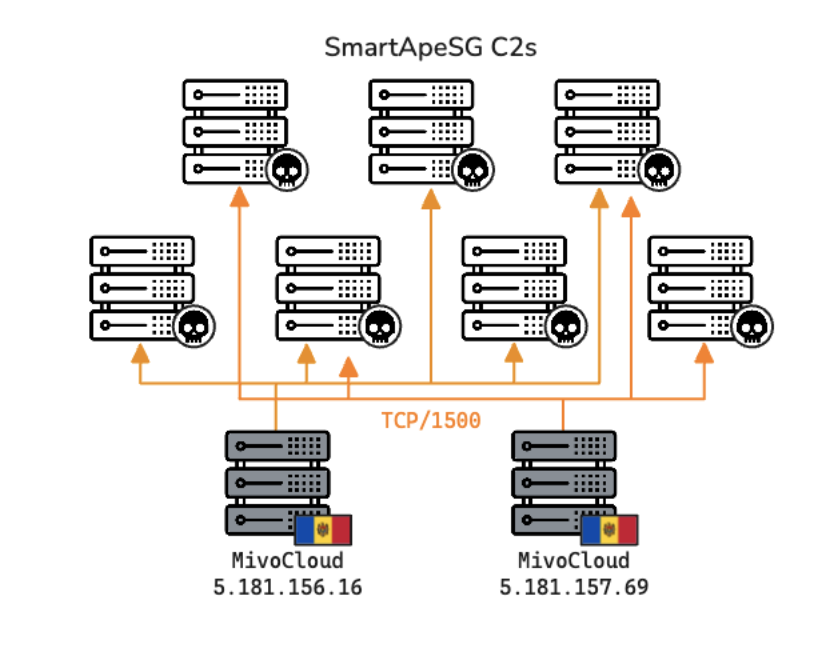
Tracing the Path From SmartApeSG to NetSupport RAT

NetFlow & Traffic Intelligence
February 3, 2025
Investigation reveals how SmartApeSG delivers NetSupport RAT, exposing links to RAT clusters, crypto services, and suspicious infrastructure. Learn more.
Malware
Real-Time Intelligence
C2 Infrastructure
Threat Actor Infrastructure
Malicious Infrastructure
Threat Hunter
Threat Intelligence Analyst
All Verticals
David Monnier

Building a More Resilient Security Strategy Through Threat Intelligence Integration

Executive Strategy, Risk & ROI
January 24, 2025
Strengthen your security strategy by integrating threat intelligence to improve response, reduce risk, and build proactive defenses amid rising cyber threats.
Visibility Gaps
Finished Intelligence Limitations
Preemptive Defense
Proactive Threat Intelligence
Real-Time Intelligence
CISO
Threat Intelligence Analyst
All Verticals
Lewis Henderson

Eating Your Own Dog Food

Real-Time Threat Detection & Signals
January 2, 2025
Explore how Team Cymru's SecOps team uses its own threat intel tools—Scout, Recon, and more—for faster investigations, proactive hunting, and automation.
Proactive Threat Intelligence
Real-Time Intelligence
Preemptive Defense
Malicious Infrastructure
Compromised Hosts
SOC Analyst
SOC Manager
All Verticals
Lewis Henderson

DORA Regulation (Digital Operational Resilience Act): A Threat Intelligence Perspective

Threat Hunting & Detection Engineering
January 2, 2025
Discover DORA compliance from a threat intel lens—understand penalties, visibility gaps, and how to strengthen operational resilience before the 2025 deadline.
Proactive Threat Intelligence
Threat Actor Infrastructure
Malicious Infrastructure
C2 Infrastructure
Real-Time Intelligence
Threat Hunter
Threat Intelligence Analyst
All Verticals
Lewis Henderson

A Primer on JA4+: Empowering Threat Analysts with Better Traffic Analysis

Incident Response & Preemptive Defense
December 23, 2024
JA4+ enhances threat analysis by providing precise insights into encrypted traffic, helping analysts detect malware and anomalies faster and more accurately.
Takedown
Malware
Preemptive Defense
Proactive Threat Intelligence
Malicious Infrastructure
Incident Responder
CISO
Technology
S2 Research Team

Jingle Shells: How Virtual Offices Enable a Facade of Legitimacy

Threat Reports & Intelligence Briefings
December 20, 2024
Virtual offices provide flexibility but also enable fraudsters to establish shell companies. Learn how this trend impacts businesses and regulations globally.
Real-Time Intelligence
Proactive Threat Intelligence
Visibility Gaps
Finished Intelligence Limitations
Preemptive Defense
CISO
Broader Security Audience
All Verticals
Kyle Contorno

2024 Year in Review: Features and Improvements in Pure Signal™ Scout

Threat Hunting & Detection Engineering
December 13, 2024
Team Cymru is excited to share our accomplishments in delivering new features and improvements in Pure Signal™ Scout.
Proactive Threat Intelligence
Real-Time Intelligence
Malicious Infrastructure
Threat Intelligence Analyst
SOC Analyst
All Verticals
David Monnier

Team Cymru Honored with Third Consecutive Gold HIRE Vets Medallion Award from U.S. Department of Labor

Threat Reports & Intelligence Briefings
November 11, 2024
Team Cymru earns third consecutive Gold HIRE Vets Medallion Award, recognizing commitment to hiring, supporting, and developing veterans in meaningful careers.
Real-Time Intelligence
Proactive Threat Intelligence
Visibility Gaps
Finished Intelligence Limitations
Preemptive Defense
CISO
Broader Security Audience
All Verticals
Rob Thomas

Celebrating a Milestone - Over 1.5 Billion Daily Queries on Our IP to ASN Mapping Service

Incident Response & Preemptive Defense
November 8, 2024
Team Cymru’s IP to ASN service now handles 1.5B+ daily queries—thanks to our community for supporting our mission to save and improve human lives.
Takedown
Malicious Infrastructure
Preemptive Defense
Proactive Threat Intelligence
Threat Actor Infrastructure
Chief Fraud Officer
Incident Responder
Government
S2 Research Team

Team Cymru Supports INTERPOL’s Operation Synergia II to Dismantle 22,000 Cybercrime Servers

Incident Response & Preemptive Defense
November 5, 2024
Team Cymru helped INTERPOL dismantle 22K cybercrime servers across 95 countries in Operation Synergia II, disrupting phishing, malware, and ransomware threats.
Takedown
Ransomware
Dark Web Monitoring
Preemptive Defense
Proactive Threat Intelligence
Incident Responder
CISO
Government
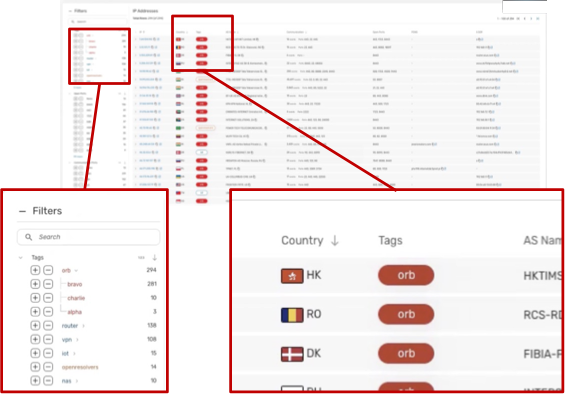
Introduction to Operational Relay Box (ORB) networks used by threat actors to obscure malicious activity
S2 Research Team

An Introduction to Operational Relay Box (ORB) Networks - Unpatched, Forgotten, and Obscured

Threat Actor, Campaign & Infrastructure Intelligence
October 29, 2024
Explore how threat actors use Operational Relay Box (ORB) networks to evade detection, hide malicious activity, and complicate cyber defense efforts. Talk to an expert.
Orb Networks
Threat Actor Infrastructure
Malicious Infrastructure
APT
Proactive Threat Intelligence
Threat Intelligence Analyst
Threat Hunter
All Verticals
Dan Schoenbaum

Announcing the Team Cymru Scout Integration With Palo Alto Cortex XSOAR

SOC Enablement & Intelligence Enrichment
October 26, 2024
Enhance threat response with Team Cymru Scout’s IP and domain intelligence, now integrated into Palo Alto Cortex XSOAR for automation and real-time insights.
Malicious Infrastructure
Proactive Threat Intelligence
Real-Time Intelligence
Compromised Hosts
C2 Infrastructure
Threat Hunter
SOC Manager
Technology
tcblogposts

Talent and Technology: Bridging the Gap in Modern Threat Hunting Programs

Threat Hunting & Detection Engineering
September 17, 2024
Discover how the right tools and trained analysts can boost threat hunting and shift your security program from reactive defense to proactive reconnaissance.
C2 Infrastructure
Malicious Infrastructure
Threat Actor Infrastructure
APT
Proactive Threat Intelligence
Incident Responder
Threat Intelligence Analyst
All Verticals
tcblogposts

What is Threat Intelligence?

Malware & Ransomware Analysis
September 14, 2024
Learn what threat intelligence is, why it matters, and how it helps organizations detect, prevent, and respond to cyber threats with real-time, actionable insights.
Malware
Ransomware
Botnets
C2 Infrastructure
Compromised Hosts
Malware Researcher
Incident Responder
Financial Services
tcblogposts

How Effective Threat Hunting Programs are Shaping Cybersecurity

Threat Hunting & Detection Engineering
September 10, 2024
Boost cybersecurity with better threat hunting. Explore how tools, talent, and data help teams detect and prevent threats earlier. Visit our website.
Proactive Threat Intelligence
Threat Actor Infrastructure
Malicious Infrastructure
C2 Infrastructure
Real-Time Intelligence
Threat Hunter
Threat Intelligence Analyst
All Verticals
tcblogposts

The Evolution of Threat Hunting

Threat Reports & Intelligence Briefings
September 3, 2024
Discover how 2024's threat hunting programs are evolving with better tools, skilled analysts, and proactive strategies to stay ahead of cyber threats. Talk to an expert.
Real-Time Intelligence
Proactive Threat Intelligence
Visibility Gaps
Finished Intelligence Limitations
Preemptive Defense
CISO
Broader Security Audience
Technology
S2 Research Team

Insights into a “Cyber Attack” against the Venezuelan National Electoral Council

Malware & Ransomware Analysis
August 29, 2024
Analyze the suspected cyber attack on Venezuela's National Electoral Council during the 2024 elections, including network traffic and DDoS attack insights.
Ransomware
Malware
Botnets
C2 Infrastructure
Compromised Hosts
Malware Researcher
Incident Responder
All Verticals
tcblogposts

How Security Teams are Strengthening Their Threat Hunting

Threat Hunting & Detection Engineering
August 27, 2024
Discover how security teams are strengthening their threat hunting programs with the right tools, training, and strategies to proactively prevent cyber attacks.
Proactive Threat Intelligence
Threat Actor Infrastructure
Malicious Infrastructure
C2 Infrastructure
Real-Time Intelligence
Threat Hunter
Threat Intelligence Analyst
All Verticals
S2 Research Team

FIN7: The Truth Doesn't Need to be so STARK

Incident Response & Preemptive Defense
August 13, 2024
Explore how Silent Push, Stark, and Team Cymru joined forces to disrupt FIN7’s malicious activities and uncover critical threat intelligence. Learn more.
Takedown
Proactive Threat Intelligence
Malicious Infrastructure
Threat Actor Infrastructure
Real-Time Intelligence
Threat Intelligence Analyst
Incident Responder
All Verticals
S2 Research Team

Botnet 7777: Are You Betting on a Compromised Router?

Threat Reports & Intelligence Briefings
August 8, 2024
Quad7 botnet evolves: Over 12K infected routers found, including new ASUS-based 63256 bots. Learn how to identify, track, and defend against this threat.
Real-Time Intelligence
Proactive Threat Intelligence
Visibility Gaps
Finished Intelligence Limitations
Preemptive Defense
CISO
Broader Security Audience
Technology
tcblogposts

Navigating the Evolving Landscape of Cybersecurity

Attack Surface & Exposure Visibility
July 31, 2024
Discover how organizations are advancing vulnerability management using EPSS and KEV to better assess exploitability and reduce cyber risk. Learn more.
Real-Time Intelligence
Proactive Threat Intelligence
Preemptive Defense
Visibility Gaps
Threat Actor Infrastructure
Broader Security Audience
All Audiences
All Verticals
Dan Schoenbaum

How the New Splunk App for Scout Can Enrich and Accelerate Your Investigations

SOC Enablement & Intelligence Enrichment
June 21, 2024
Add real-time threat data to Splunk with the Team Cymru Scout App and simplify investigations using enriched dashboards and IP/domain insights. Read more.
Real-Time Intelligence
Compromised Hosts
C2 Infrastructure
Visibility Gaps
Proactive Threat Intelligence
SOC Manager
Security Architect
All Verticals
tcblogposts

The Importance of Real-Time Insights for SOC Security Analysts

SOC Enablement & Intelligence Enrichment
June 7, 2024
Empower SOC analysts with real-time intelligence to improve detection, reduce alert fatigue, and increase productivity and team value. Learn more about our services.
Real-Time Intelligence
Compromised Hosts
C2 Infrastructure
Visibility Gaps
Proactive Threat Intelligence
SOC Manager
Security Architect
Technology
A useful analogy for understanding NetFlow network traffic data
tcblogposts

Want to learn more about NetFlow? Here's a useful analogy to get you started

NetFlow & Traffic Intelligence
May 22, 2024
Explore how NetFlow helps monitor network traffic. A clever analogy in this blog makes a complex topic simple, engaging, and easy to grasp.
Real-Time Intelligence
C2 Infrastructure
Threat Actor Infrastructure
Malicious Infrastructure
Visibility Gaps
Threat Hunter
Threat Intelligence Analyst
All Verticals
S2 Research Team

Latrodectus: This Spider Bytes Like Ice

Threat Reports & Intelligence Briefings
April 4, 2024
Explore new research on Latrodectus, a rising malware linked to IcedID. Learn how it evades detection and why threat actors are adopting it fast.
Real-Time Intelligence
Proactive Threat Intelligence
Visibility Gaps
Finished Intelligence Limitations
Preemptive Defense
CISO
Broader Security Audience
Technology
S2 Research Team

Insights into Internet Outages along Africa's Western Coast

Threat Reports & Intelligence Briefings
March 26, 2024
Major internet outages hit 13 African nations in March 2024. Our analysis reveals traffic patterns, ongoing impacts, and connectivity insights from Pure Signal™.
Real-Time Intelligence
Proactive Threat Intelligence
Visibility Gaps
Finished Intelligence Limitations
Preemptive Defense
CISO
Broader Security Audience
All Verticals
Lewis Henderson

Peer Reviews - Why Peer Reviews Matter

Events, Conferences & Community Engagement
March 15, 2024
Explore Pure Signal product reviews from real users. Find out how to share your anonymous feedback and help improve cybersecurity tools you rely on.
C2 Infrastructure
Malicious Infrastructure
Threat Actor Infrastructure
APT
Proactive Threat Intelligence
Threat Intelligence Analyst
Threat Hunter
All Verticals
tcblogposts

Threat Intelligence: A CISO ROI Guide - Elite Threat Hunters Prevent Supply Chain Breaches

Executive Strategy, Risk & ROI
March 13, 2024
Discover how elite threat hunters and Pure Signal Recon help CISOs prevent supply chain breaches, save millions, and boost security ROI. Learn more.
Malicious Infrastructure
Threat Actor Infrastructure
APT
Proactive Threat Intelligence
Real-Time Intelligence
Threat Intelligence Analyst
Threat Hunter
Technology
Lewis Henderson

Senior Stakeholder explainer for Octo Malware

SOC Enablement & Intelligence Enrichment
March 9, 2024
Octo malware threatens financial and corporate data. Learn why senior stakeholders need a multi-layered defense to protect against this growing risk.
Malicious Infrastructure
Real-Time Intelligence
Compromised Hosts
C2 Infrastructure
Visibility Gaps
SOC Manager
Security Architect
Financial Services
S2 Research Team

Coper / Octo - A Conductor for Mobile Mayhem… With Eight Limbs?

Malware & Ransomware Analysis
March 6, 2024
Explore Coper/Octo, an Android malware-as-a-service evolved from Exobot, targeting users globally with remote access, keylogging, and SMS interception. Contact us.
Dark Web Monitoring
Real-Time Intelligence
Proactive Threat Intelligence
Preemptive Defense
Visibility Gaps
Broader Security Audience
All Audiences
All Verticals
Steve Santorelli

Navigating Cybersecurity Frontiers in Rwanda: Unveiling the RISE Conference's Agenda

Real-Time Threat Detection & Signals
February 22, 2024
Discover how RISE 2024 Rwanda unites cyber experts to tackle Africa’s growing digital threats through collaboration, innovation, and policy insights. Read more.
Real-Time Intelligence
Proactive Threat Intelligence
Preemptive Defense
Malicious Infrastructure
Compromised Hosts
Threat Intelligence Analyst
All Verticals
Lewis Henderson

Continuous Threats Need Continuous Management

AI-Driven Threats & Autonomous Security
February 22, 2024
Explore why CTEM is essential for modern cyber defense - helping CISOs cut breach risk, optimize security ROI, and strengthen cross-functional alignment.
Real-Time Intelligence
Proactive Threat Intelligence
Malicious Infrastructure
Threat Actor Infrastructure
Preemptive Defense
Threat Intelligence Analyst
Security Architect
All Verticals
Lewis Henderson

Risk Modeling and Real-Time Intelligence - Part 2

Threat Hunting & Detection Engineering
December 15, 2023
Learn how NIST 2.0 supports smarter risk modeling, supply chain security, and real-time intelligence to protect organizations of all sizes from cyber threats.
Malicious Infrastructure
Proactive Threat Intelligence
Threat Actor Infrastructure
C2 Infrastructure
Real-Time Intelligence
Threat Hunter
Threat Intelligence Analyst
All Verticals
Lewis Henderson

Risk Modeling and Real-Time Intelligence - Part 1

Threat Reports & Intelligence Briefings
November 29, 2023
Discover how DPRM solutions enhance cyber risk models, helping you assess vulnerabilities, prioritize threats, and support smart business decisions. Talk to an expert.
Real-Time Intelligence
Proactive Threat Intelligence
Visibility Gaps
Finished Intelligence Limitations
Preemptive Defense
CISO
Broader Security Audience
All Verticals
Lewis Henderson

Threat Modeling and Real-Time Intelligence - Part 2

SOC Enablement & Intelligence Enrichment
November 13, 2023
Discover how real-time threat intel complements MITRE ATT&CK, offering dynamic visibility into adversaries and helping analysts outpace evolving threats.
Real-Time Intelligence
Compromised Hosts
C2 Infrastructure
Visibility Gaps
Proactive Threat Intelligence
SOC Manager
Security Architect
All Verticals
Lewis Henderson

Threat Modeling and Real-Time Intelligence - Part 1

Threat Actor, Campaign & Infrastructure Intelligence
November 3, 2023
Explore how real-time threat intelligence enhances threat modeling to proactively defend apps, infrastructure, and digital services from evolving cyber threats.
Real-Time Intelligence
Malicious Infrastructure
Threat Actor Infrastructure
APT
Proactive Threat Intelligence
Threat Intelligence Analyst
Threat Hunter
All Verticals

Stay in the loop

Stay current with Team Cymru insights

Get the latest research, articles, and threat intelligence resources, delivered straight to your inbox.

See the infrastructure behind the headlines

Every post starts in the same global telemetry Team Cymru customers use. Bring our analysts the investigation you are working on.